The Octri Blog
News, guides & deep-dives
Product updates and practical writing on API documentation, SDKs, and developer experience.
Showing articles tagged #api-security.
Engineering3 min read
Your MCP server authenticates users. Does it preserve their permissions?
Follow identity from MCP client to downstream API. Check token audiences, delegated credentials and tenant authorization at each boundary.
Engineering3 min read
Where does an API key go when someone clicks Try it?
Follow credentials through a documentation playground. Check browser storage, request destinations, proxy behavior and logs.
Engineering6 min read
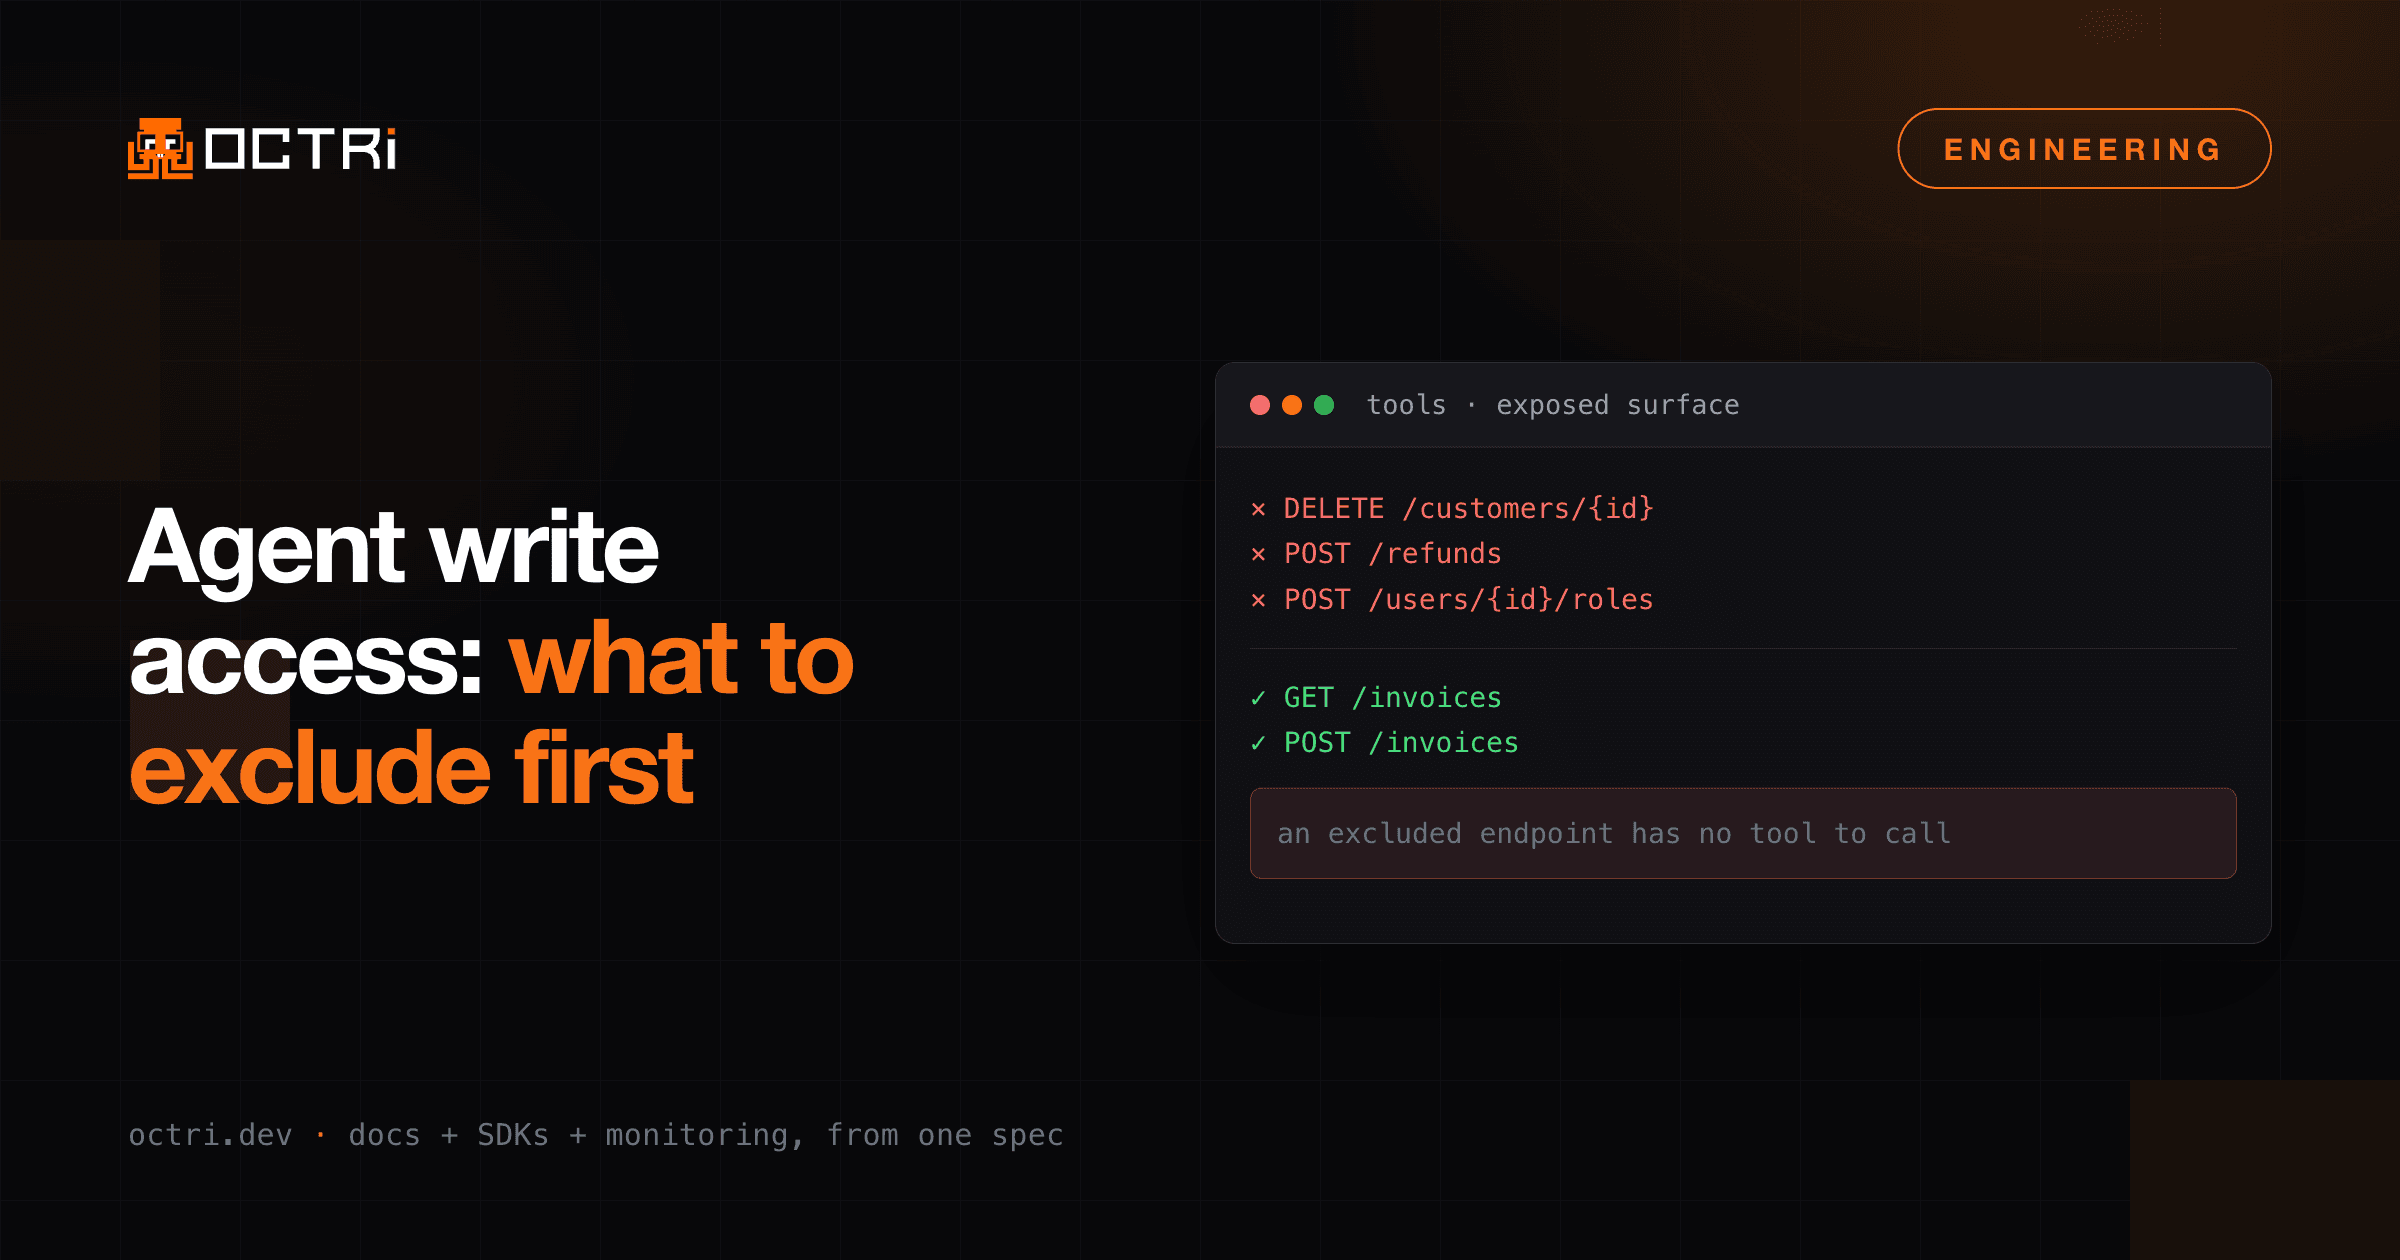
Giving an agent write access to your API: what to exclude first
A tool call is a real request against a real API. Before you connect one, the question is not which endpoints to expose. It is which ones an agent must never reach.
Engineering5 min read
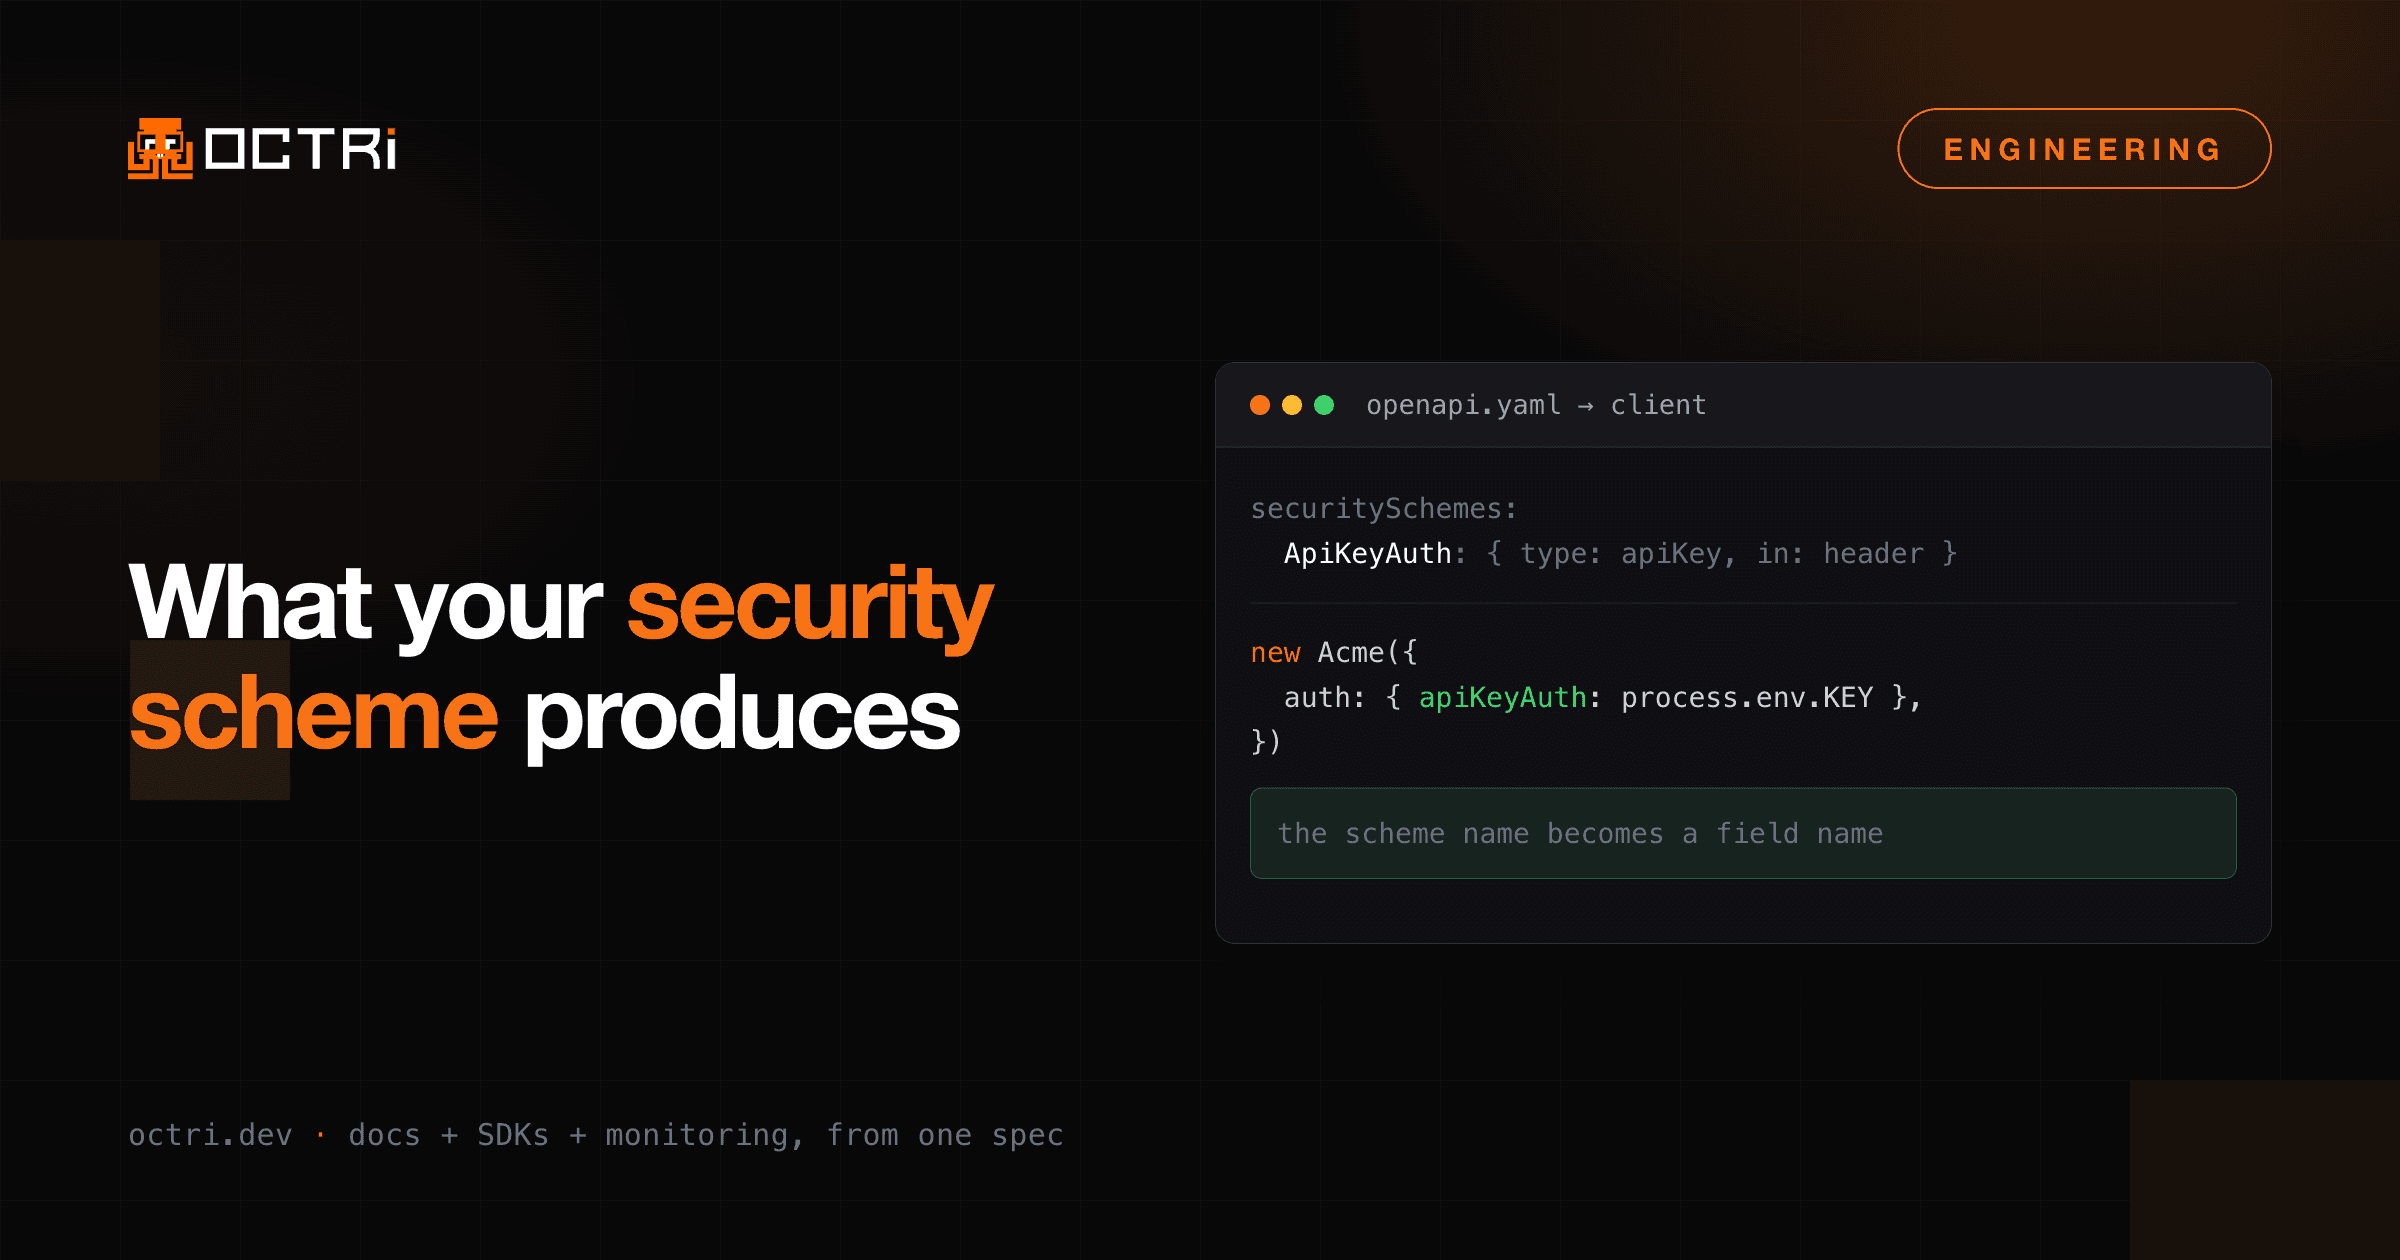
What your OpenAPI security scheme actually produces in an SDK
A security scheme is not documentation. It is the auth configuration your generated client ships with, and a spec that declares none produces a client with no way to authenticate.